When businesses talk about security compliance, it often sounds complex and technical.
But the goal is actually very simple:
Prove that your servers are secure, trustworthy, and professionally managed.
This guide explains CIS Benchmarks in plain language, designed for non-technical decision-makers, auditors, and enterprise clients.
🔍 What Are CIS Benchmarks? (In Simple Words)
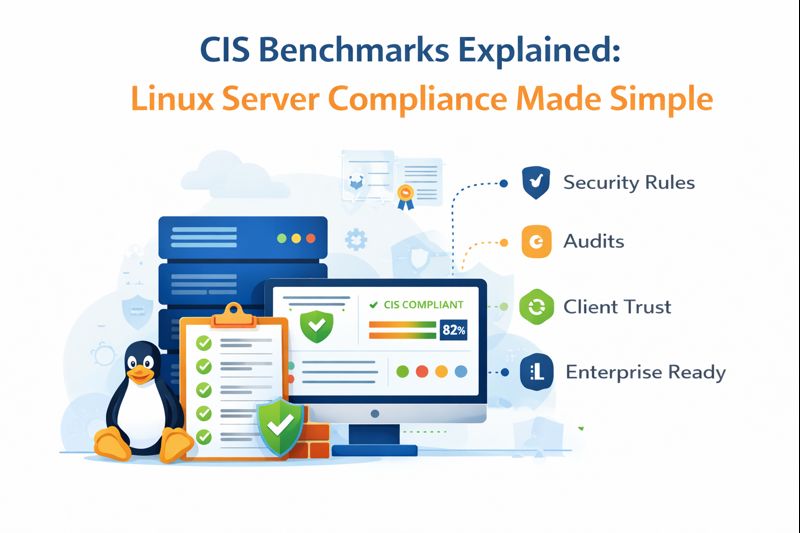
CIS Benchmarks are security best-practice rules created by global cybersecurity experts.
Think of them as:
- A security checklist for servers
- A standard rulebook auditors trust
- A proof of responsibility for enterprises
If your Linux server follows CIS Benchmarks, it means:
- Common security risks are reduced
- Misconfigurations are fixed
- The system follows globally accepted standards
🧠 Why CIS Benchmarks Matter for Businesses
Even if your server “works fine”, that does not mean it is secure.
CIS Benchmarks help answer critical questions like:
- Are unnecessary services disabled?
- Are login rules strict enough?
- Are logs recorded properly?
- Is access limited to the right people?
👉 These are the exact questions auditors, partners, and enterprise clients ask.
⚙️ How CIS Compliance Works (Without Technical Jargon)
1️⃣ Standard Security Rules
CIS provides a list of recommended settings, such as:
- Strong access controls
- Safe default configurations
- Proper logging
- Reduced attack surface
No guesswork. No opinions.
2️⃣ Server Is Checked Against the Rules
Your server is reviewed to see:
- Which rules are followed
- Which rules are missing
- Which areas are risky
This creates a compliance score.
3️⃣ Gaps Are Identified
Instead of vague warnings, you get:
- Clear pass / fail results
- Risk level (Low / Medium / High)
- Actionable improvement points
4️⃣ Continuous Monitoring (Project Advantage)
In modern setups (like your platform):
- Compliance is not a one-time audit
- Changes are monitored continuously
- Deviations are detected early
This is enterprise-grade readiness.
⚠️ Risks of Ignoring CIS Benchmarks
Without CIS-aligned security:
❌ Higher chance of breaches
❌ Failed audits
❌ Loss of enterprise trust
❌ Vendor rejection
❌ Compliance penalties
❌ Reputation damage
Many companies lose deals not because of hacks, but because they fail security checks.
✅ Benefits of CIS Compliance (Business View)
🔐 1. Stronger Security Foundation
Most common attacks exploit misconfigurations.
CIS directly fixes that.
📄 2. Audit & Compliance Readiness
Auditors recognize CIS instantly.
It reduces audit friction and questioning.
🤝 3. Increased Client Trust
Enterprise clients prefer vendors who:
- Follow global standards
- Can prove security maturity
- Take compliance seriously
🏢 4. Enterprise & SaaS Readiness
CIS alignment supports:
- ISO-style controls
- SOC-type assessments
- Vendor due diligence
- Government & institutional contracts
🧘 5. Peace of Mind for Leadership
Management can confidently say:
“Our infrastructure follows globally accepted security standards.”
🧩 How This Fits Your Security Platform
Your project aligns perfectly with CIS-style compliance because:
- Servers are monitored from inside (agent-based)
- Logs and access activities are tracked automatically
- Security posture is visible via a dashboard
- Deviations are detected early
- Technical complexity stays hidden from clients
👉 This bridges the gap between technical security and business trust.
👥 Who Should Care About CIS Benchmarks?
✔ SaaS companies
✔ Enterprises
✔ Hosting providers
✔ Government & institutional projects
✔ Compliance-driven businesses
✔ Any company planning to scale
If trust matters, compliance matters.
🏁 Simple Takeaway
CIS Benchmarks turn “we think we’re secure” into
“we can prove we’re secure.”
That proof builds trust, passes audits, and unlocks enterprise opportunities.